Google Analytics Hostname Filters: A Complete GA4 Guide

Analyze how Google Analytics hostname filters work in GA4, how to set one up step-by-step, and how to block spam or fake domains from your reports.
Analyze how Google Analytics hostname filters work in GA4, how to set one up step-by-step, and how to block spam or fake domains from your reports.
Analyze how Google Analytics hostname filters work in GA4, how to set one up step-by-step, and how to block spam or fake domains from your reports.
If you've ever opened your GA4 reports and spotted traffic from a domain that isn't yours, you're not imagining things, and until recently, GA4 didn't give you a clean, native way to stop it. That changed on June 11, 2026, when Google rolled out a dedicated hostname filter, letting you exclude events that don't come from a domain you've approved.
This guide walks through what the filter does, why it exists, and exactly how to set one up without accidentally wiping out legitimate traffic.
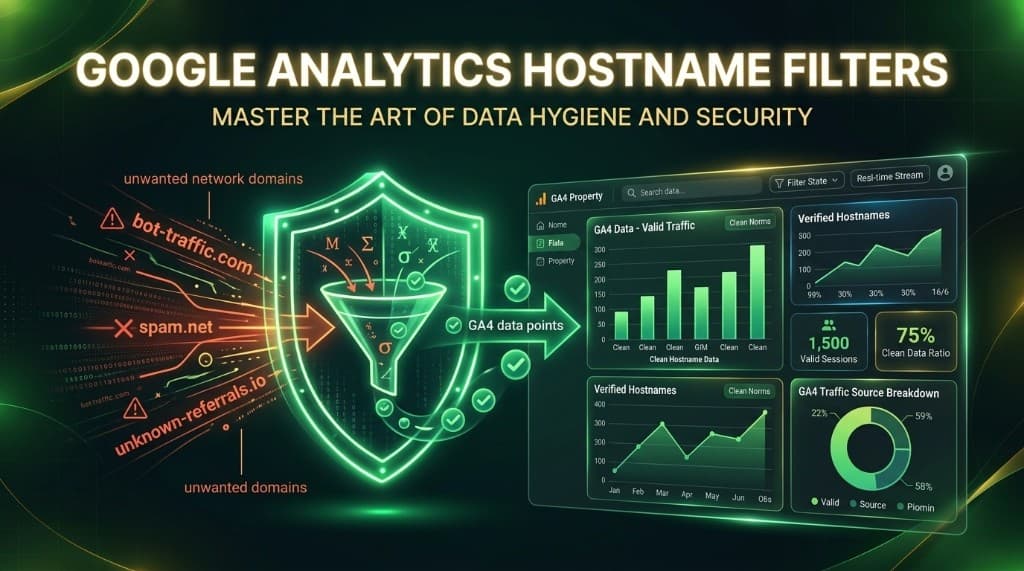
A hostname is simply the domain an event was collected on — example.com or www.example.com, for instance. A hostname filter is a property-level data filter that lets you control which events GA4 actually processes into your reports, based on that hostname. You can either block a handful of known bad domains, or flip it around and only allow data from the domains you trust.
It lives in the same place as two filters you may already know: the internal traffic filter and the developer traffic filter. You'll find all three under Admin → Data collection and modification → Data filters.
Your GA4 Measurement ID is embedded in your site's tracking code, which means it's technically visible to anyone who views your page source. Spammers sometimes copy that ID and send fake events straight into your property, either by cloning it on a lookalike site or firing hits directly at Google's collection endpoint. The result is "ghost" traffic that never actually touched your website but still shows up in your sessions, bounce rate, and conversion numbers — the exact metrics that decisions like a SEO vs. paid ads budget call often rest on.
If you're used to Universal Analytics' referral exclusion list or View-level filters, it's worth noting those don't exist anymore. UA stopped collecting new data on July 1, 2023, and Google deleted all historical UA data by mid-2024. The hostname filter is GA4's native answer to a problem that UA used to solve differently.
When you create the filter, you'll choose between two modes. Include filters are generally the safer long-term choice once you know your full hostname list, because you're not stuck chasing every new spam domain that pops up. Exclude filters are fine for a quick, targeted fix.
| Filter type | What it does | Best for |
|---|---|---|
| Exclude | Blocks only the specific hostnames you list. | A quick fix when you've already identified one or two problem domains. |
| Include only | Allows data solely from the hostnames you approve, and silently blocks everything else. | The safer long-term choice once you know your full hostname list. |
Before touching the filter, confirm what's actually hitting your property. GA4 treats example.com and www.example.com as two separate hostnames, so both need to be listed if you're using exact matching.
You'll need Editor or Administrator access to the property. There's no regex support yet, so exact matching, adding one hostname at a time, gives you the most control.
Leave the filter in Testing for at least a few days, long enough to capture traffic across your main domain, subdomains, and anything else that legitimately sends data to the property. While testing, use the Test data filter name dimension in your reports to see exactly which events would have been blocked, without actually losing any data. Only flip it to Active once you're confident nothing important is getting caught.
Once active, the filter permanently affects incoming data. Blocked events aren't recoverable, and it does not affect data already collected.
With an Exclude filter: forgetting a hostname means unwanted traffic keeps flowing through untouched. If new spam domains keep appearing, switch to an Include filter instead.
With an Include filter: forgetting a legitimate hostname, a subdomain, a payment gateway, or a staging domain your web development team still uses means that traffic silently disappears once the filter goes active. Double-check your hostname list against real report data before switching from Testing to Active.
Does it block Measurement Protocol spam? No. This is the detail most guides gloss over: events sent via the Measurement Protocol — a common vector for the exact kind of ghost spam this filter is meant to solve — bypass the include hostname filter entirely. If that's your main spam source, you'll need to protect your API secrets and address it separately. Don't rely on the hostname filter alone.
Does it clean up historical data? No. The filter only affects events collected after you activate it. To exclude bad hostnames from past reports, you'll still need a segment, comparison, or exploration filter applied manually.
Under an Include filter, events with an empty hostname are automatically blocked. That's usually a good thing — a missing hostname often signals junk traffic — but it can also catch legitimate events that don't include the page_location parameter, so it's worth checking your implementation before activating.
A property-level data filter that controls which website events GA4 processes, based on the domain they were collected on.
Usually, yes, if you know your full list of legitimate hostnames. It's less maintenance than chasing spam domains one at a time.
Yes, if both send data to your property. GA4 treats them as separate hostnames.
Under an Include filter, they're automatically blocked.
No, that traffic bypasses the hostname filter entirely.
No, it only affects data collected after activation. Use a segment or exploration for past data.